


Top 10+ Microsegmentation Tools

Microsegmentation divides networks into controlled segments, limiting the spread of breaches.
We researched 11 microsegmentation platforms, examining official product documentation, cross-referencing release notes, and field notices. Based on key features and market presence, see the top 11 microsegmentation tools:
Features
All providers offer common features and therefore can support typical microsegmentation use cases.
Vendors with:
- APT (advanced persistent threat) defense: Identify targeted threats by analyzing unusual traffic patterns
- Network topology mapping: Discover a network’s components and topology, creating a visual map of the network architecture.
See vendor selection criteria.
FireMon
FireMon is the founder of Network Security Policy Management (NSPM) and serves as the control plane for security policy across modern enterprise networks. The platform combines firewall policy management, a Zero Trust control plane, AI-powered policy control, and risk-aware policy change management to detect drift, quantify exposure, and drive prioritized corrective action.
FireMon also integrates with microsegmentation platforms, including Illumio, VMware NSX, and Akamai Guardicore Segmentation, extending governance across enforcement layers to keep segmentation policies aligned over time.1
Key features:
- Microsegmentation policy control: Governs segmentation policy in the same normalized model as firewall and cloud rules, and validates changes before enforcement.
- Security Manager: The required core of the platform, with real-time change detection, compliance reporting, and one policy database across firewalls, cloud security groups, and microsegmentation platforms.
- Risk Analyzer: Correlates vulnerability data with network access paths to prioritize which exposure matters most, given actual reachability.
- Policy Planner: Automates change workflows with built-in risk assessment before policy changes are deployed.
- Agentic AI: Insights answers policy questions in plain language, and FireMon Agentic AI prepares change recommendations for practitioner review.
- Cloud policy governance: Reviews AWS, Azure, and Google Cloud security groups in the same policy model as on-prem firewalls.
- Integrations: Connects with ITSM, SIEM/SOAR, and vulnerability scanners,2 and with microsegmentation platforms including Illumio, VMware NSX, and Akamai Guardicore.3
Pros
- Policy cleanup: Policy Optimizer flags overly permissive, expired, and unused rules and routes each review to the rule owner.4
- Centralized visibility: Security Manager keeps one policy database across on-prem firewalls, cloud security groups, and microsegmentation platforms.5
- Rule search: FireMon’s SIQL query language searches rules, devices, and cloud security groups in real time.2
- Rule reduction: FireMon reports a 37% average rule reduction and says most customers reclaim 30-40% of their rule base within the first month.6
Cons
- Enforcement: FireMon governs segmentation policy and does not replace a microsegmentation platform, so it needs an enforcement tool such as Illumio, VMware NSX, or Akamai Guardicore.7
- Integration depth: Support levels vary by platform. FireMon lists VMware NSX-T at all five levels, Illumio PCE at three, and Akamai Guardicore at two.3
- Modular licensing: Every deployment requires Security Manager, and Policy Planner, Policy Optimizer, and Risk Analyzer are add-on modules.8
Tufin
Tufin works across different vendors’ devices and platforms, which is useful when you’re managing equipment from multiple manufacturers. This vendor-agnostic approach gives visibility across diverse network components.
SecureTrack+ measures live network behavior against defined segmentation zones, flags violations, and manages exceptions.9
Key features:
- Network change management: Monitor information about your organization’s network devices by documenting configurations.
- Network security policy management: Manage policies to secure firewalls, networks, and assets against unapproved access.
- Firewall orchestration: Execute a centralized security management layer to implement security policies across firewalls.
- Akamai Guardicore integration: Joint solution unifies Akamai Guardicore Segmentation’s workload-level enforcement with Tufin’s centralized policy control plane, providing governance across firewalls, cloud, SASE, and microsegmentation in a single view.10
Best practices:
Implement and monitor network microsegments: Users can identify access violations across microsegments by using a corporate matrix, and choose to delete them or mark them as temporary deviations.
Define zero-trust zones: Users can enable zero-trust cloud network access with Tufin.
Create a policy with Tufin:
Users can type a “policy name” and select the following:
- Compliance policy type
- Devices to which the compliance policy will apply
- Recipients to receive alerts when the installed policy conflicts with this compliance policy
Pros
- Segmentation policy: SecureTrack+ defines segmentation zones across devices and manages traffic between them through a central policy matrix.9
- Device coverage: SecureTrack+ centralizes policy management across firewalls, NGFWs, routers, switches, SDN, and hybrid cloud.9
- Microsegmentation monitoring: TOS supports Guardicore and Illumio microsegmentation workloads.11
- Change automation: SecureChange, the built-in ticketing system of TOS, provides customizable change workflows with varying levels of automation.12
Cons
- Transparent firewalls: Firewalls in transparent mode have no routing information, so they stay off the Map until an administrator adds them.13
- Unmonitored devices: Devices that SecureTrack does not monitor stay out of topology calculations unless an administrator adds them as generic devices with interface and routing data.14
- Licensing: Firewall units, cloud VMs, and microsegmentation workloads are licensed separately. One microsegmentation license covers one server or up to five endpoints, sold in blocks of 100.
Cisco Identity Services Engine
Cisco ISE combines microsegmentation with network access control (NAC).
Pros
- Network access control: The Essentials tier includes AAA and 802.1X authentication.15
- Group-based segmentation: The Advantage tier adds TrustSec group-based policy, profiling, and pxGrid context sharing.
- Posture: The Premier tier adds posture, MDM compliance, and threat-centric network access control.15
Cons
- Licensing: Segmentation with TrustSec needs the Advantage tier, and each virtual or cloud-deployed node needs its own VM license.
- Cloud upgrades: Native cloud deployments must upgrade through backup and restore.16
AlgoSec
AlgoSec monitors networks, connects firewall rules with business applications, and detects compliance anomalies using its IP engine.
Pros
- Firewall rules: Horizon Security Analyzer identifies risky rules, the assets they expose, and whether those rules are in use.17
- Automation: It finds unused, duplicate, overlapping, and expired rules, and Horizon FireFlow automates the security policy change process.
- Application mapping: AppViz associates each firewall rule with the business applications it supports.
Cons
- Unused-rule analysis: Detection relies on log data for devices such as Check Point and Juniper, and AFA keeps 60 days of logs by default.18
- Centralized console: Unified Security Management provides visibility, policy management, logging, and reporting across hybrid clouds and on-premises from one console.
Cons
- Management dependency: Gateways need a Security Management Server, and Check Point recommends Smart-1 Cloud for autoscaling deployments on Google Cloud.19
VMware NSX
Handles microsegmentation, network security, software-defined networking, and private cloud deployment. Helps transition from physical to virtual infrastructure through network virtualization.
Pros
- Layer 7 policy: Policies support application identity, user identity, and FQDN filtering.20
- Illumio Insights Network Posture: AI security graph enhancement that provides system-wide, real-time visibility of lateral movement risk across hybrid, multi-cloud, and OT environments surfacing end-to-end attack paths for prioritized containment.21
Pros
- Phased rollout: Workloads move from Idle to Visibility Only, Selective, and Full enforcement. Visibility Only reports traffic flows without blocking them.22
- Traffic visualization: The Illumination map shows traffic as allowed, potentially blocked, or blocked.23
- Label-based policy: Rules reach a workload when the policy and the workload share the same labels.
Cons
- Agent dependency: The VEN enforces policy by managing each workload’s native host firewall. Where a VEN cannot be installed, the workload exists only as an unmanaged workload with no VEN.23
- Host firewall control: In Exclusive mode, Illumio disables Windows Advanced Firewall policy and deletes all non-Illumio filters on Linux nftables.24
Zscaler Private Access (ZPA)
Founded in 2007. 11K+ customers, including 40%+ of the Forbes Global 2000.25
Cons
- Windows firewall conflicts: In Windows Firewall (WAF) mode, agents cannot reliably enforce policy when a third-party firewall is present.26
- Platform gaps: AIX enforcement has no IPv6 support, and Windows Kubernetes pods do not support application, user, or service-based policies.
- On-premises capacity: Hardware appliances top out at 10,000 workloads (medium) and 37,500 (large) in detailed mode.
Nutanix Flow Network Security
Nutanix Flow Network Security (FNS) is Nutanix’s microsegmentation product. It is built into the AHV hypervisor and included with NCI Pro and Ultimate. Flow Virtual Networking, also called Advanced Networking, is the overlay networking service that must be enabled when Microsegmentation is first enabled.
Pros
- Category-based policy: Policies use dynamic categories instead of static IP addresses.
- Policy testing: FNS maps application workflows at port level and monitors policy impact before enforcement.
Cons
- Hypervisor scope: FNS Next-Gen 7.5 runs only on AHV clusters.27
- Memory overhead: Enabling FNS adds 2 GB to each Prism Central VM, plus 3 GB of userspace and 1 GB of kernel memory on every AHV host.27
What is microsegmentation?
Microsegmentation is a security approach that divides data based on workload within an organization’s network. Security architects can create protocols that define how all traffic flows north-south and east-west.
Benefits of microsegmentation tools
1. Reduced attack surface
By isolating individual assets, microsegmentation minimizes the risk that an attacker can access multiple resources. Illumio helped Hi-Temp Insulation reduce its attack surface by applying segmentation policies that protected sensitive customer data.
2. Compliance with regulatory standards
Microsegmentation helps companies meet regulatory requirements, such as the GDPR, by ensuring sensitive data is not breached. Cisco enabled Frankfurter Bankgesellschaft, a Zurich-based Swiss private bank, to maintain compliance with data protection laws by securing their cloud environment with detailed segmentation rules.
3. Granular policy control
Microsegmentation provides detailed control over network policies, allowing businesses to define security policies based on users, applications, or workloads. VMware enabled the California Department of Water Resources to implement granular controls for healthcare applications, reducing the risk of data breaches.
4. Enhanced cloud security
In cloud environments, microsegmentation ensures that workloads in different virtual machines or containers are isolated. Illumio used microsegmentation to help a leading hospital network in Brazil secure its cloud infrastructure, preventing unauthorized access to sensitive data.
 Add as preferred source
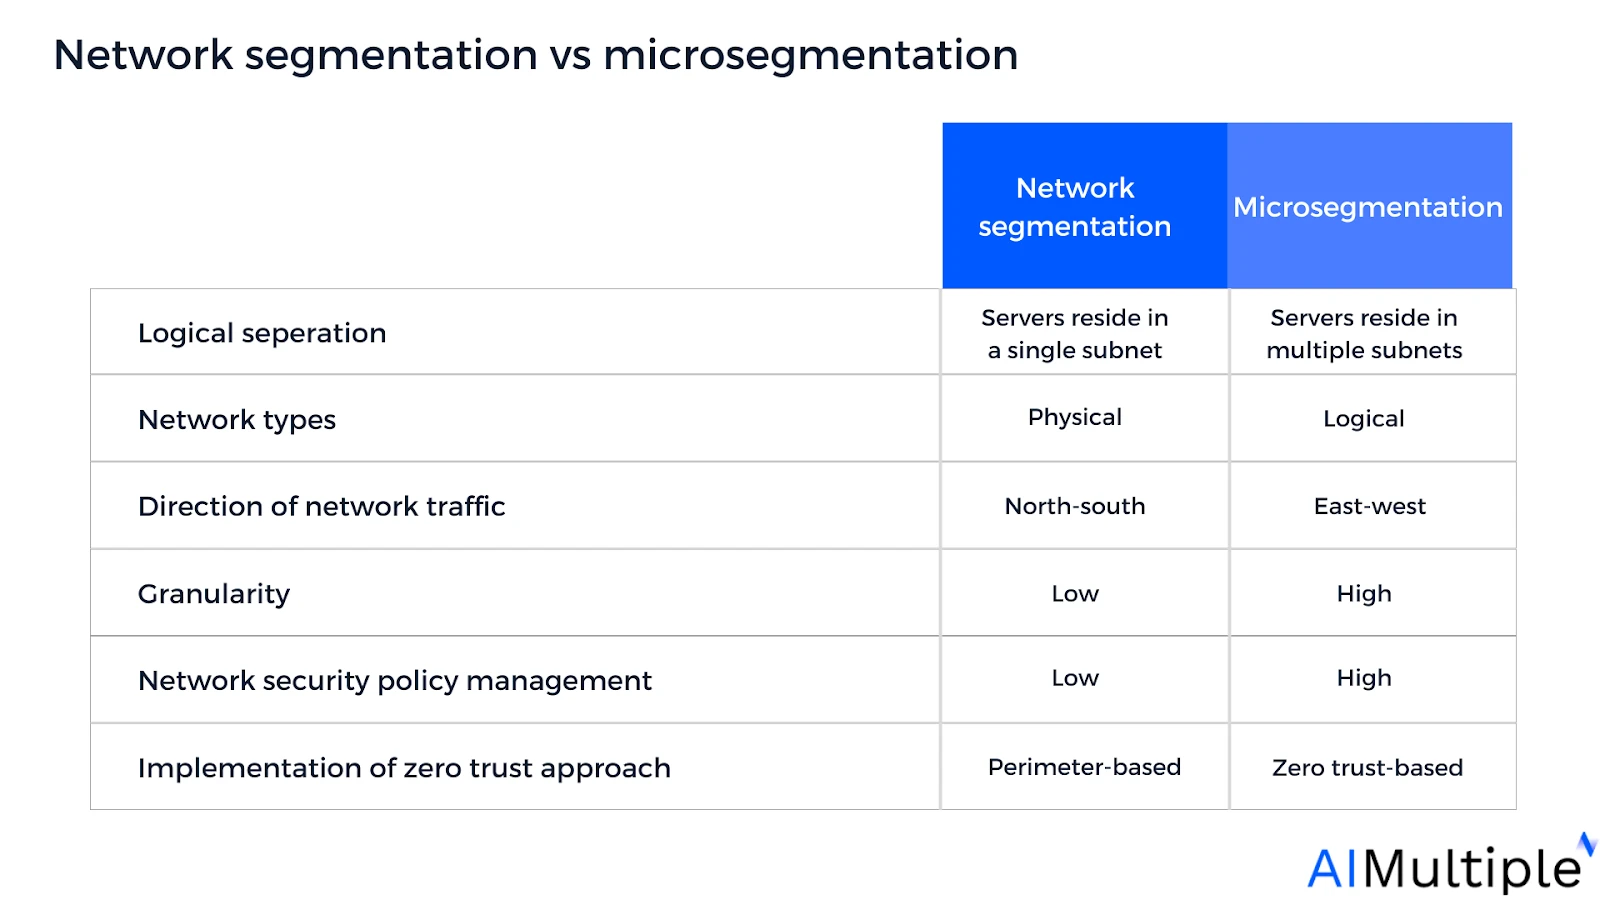
Network segmentation vs microsegmentation
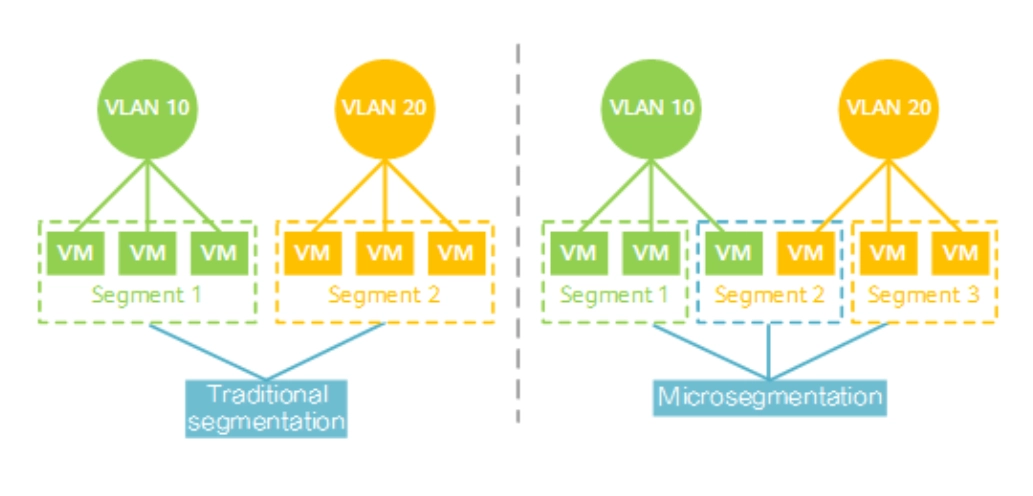
- Network segmentation enforces traditional castle-to-moat policies that leverage firewall rules at network boundaries
- Microsegmentation creates security zones that can be configured down to the host (computer) level across individual subnets.
Comparison between network segmentation and microsegmentation – using VLANs –
Source: Huawei28
Who should use traditional network segmentation?
SMEs needing budget-friendly options, overarching infrastructure security without detailed application-level configurations, simple networks with basic security needs, or solutions matching limited technical staff.
Key parameters for choosing between network segmentation and microsegmentation:
- Business scope: Implementing microsegmentation across core business areas can significantly reduce the lateral spread of a ransomware attack. Companies with numerous branches may choose microsegmentation to control intra-network traffic.
- Level of security needed: Organizations with high network security needs, such as Fortune 1000 companies, global banks, or MNCs, may select microsegmentation for finer-grained management and application-level security.
- Network complexity: 35% of IT specialists say that network complexity is an obstacle when segmenting their network. Organizations with less complex networks may use traditional segmentation.
- Financial budget: Microsegmentation integration with a security stack is expected to cost between $40K to $100K on average. Companies with limited budgets and older infrastructure may opt for network segmentation.
- Skilled labor availability: ~40% of IT specialists report a lack of skills and expertise as their main issue when implementing microsegmentation. Companies with limited technical staff may select traditional network segmentation.
Vendor selection criteria
- Number of reviews: 10+ total reviews on Gartner, G2, PeerSpot, and TrustRadius.
- Average rating: Above 4.0/5 on Gartner, G2, PeerSpot, and TrustRadius.
- Sorting: Vendors are sorted by the total number of reviews in descending order, except for subscribers to our benchmarking services.
Microsegmentation software features
Unique Features
Offered by one or a few vendors:
- Firewall orchestration: Centralized firewall management and configuration
- Day 2 network operations: Authenticates application-focused traffic/routes, firewalls, and ACLs health
- Hybrid cloud management: Manages segmentation across cloud and on-premises
- Medical network access control: Safeguards medical devices and patient records
- Runtime protection: Instant security for cloud-based tasks, web apps, and APIs
- Multi-tenancy: Secure multi-tenant isolation with self-service provisioning and IP preservation
Transparency: AIMultiple works with emerging tech vendors, including Tufin.
Common Features
All vendors provide:
- Network visibility and discovery: Instant insight into security changes and breaches
- Zero trust: No default trust, including for those inside the perimeter
- Threat detection and response: Monitors data using machine learning and behavioral analysis
- Compliance support: Maintains policies governing IT system integrity
Further Reading
- Top Firewall Management Tools: Analysis & Comparison
- Top 5 Network Security Policy Management Solutions
- Top 10+ SOAR Platforms
Cite this research
Pick the format that matches where you're publishing. Pasting the link version into your CMS preserves the backlink.
@misc{dilmegani2026,
  author = {Dilmegani, Cem and Arslan, Ezgi},
  title  = {{Top 10+ Microsegmentation Tools}},
  year   = {2026},
  month  = jul,
  howpublished    = {\url{https://aimultiple.com/microsegmentation-tools}},
  note   = {AIMultiple. Retrieved July 16, 2026}
}Results and timestamps of 11 data points. Download the summary data shown in this article's charts and tables as a ZIP file containing one CSV file.
Want the granular data behind it? Join Premium
Changelog
12 updatesAdded FireMon as an eleventh vendor to the microsegmentation tools list, and removed the AlgoSec adoption statistics.
Added Akamai Guardicore integration to Tufin's features.
Reference Links
Cem's work at AIMultiple has been cited by leading global publications including Business Insider, Forbes, Morning Brew, and Washington Post, global firms like Deloitte and HPE, NGOs like World Economic Forum, and supranational organizations like European Commission. [1], [2], [3], [4], [5]
Throughout his career, Cem served as a tech consultant, tech buyer and tech entrepreneur. He advised enterprises on their technology decisions at McKinsey & Company and Altman Solon for more than a decade. He also published a McKinsey report on digitalization.
He led technology strategy and procurement of a telco while reporting to the CEO. He has also led commercial growth of deep tech company Hypatos that reached a 7 digit annual recurring revenue and a 9 digit valuation from 0 within 2 years. Cem's work in Hypatos was covered by leading technology publications like TechCrunch and Business Insider.
Cem regularly speaks at international technology conferences. He graduated from Bogazici University as a computer engineer and holds an MBA from Columbia Business School.







Be the first to comment
Your email address will not be published. All fields are required. Comments are left in their original language.